Skip to content
| Marketplace
Sign in
Visual Studio Code>Linters>DeepSweep: AI Agent Security & Code ReviewNew to Visual Studio Code? Get it now.
DeepSweep: AI Agent Security & Code Review

DeepSweep: AI Agent Security & Code Review

DeepSweep AI

|
4 installs
| (0) | Free
The Agent Evidence Layer for AI coding agents. A flight recorder and circuit breaker for your workflow. Your AI agents have shell access, repo write permissions, and your credentials. Do you actually know what they're doing? DeepSweep is sub-second, local-first agent security that reviews what your
Installation
Launch VS Code Quick Open (Ctrl+P), paste the following command, and press enter.
Copied to clipboard
More Info

DeepSweep - Runtime Governance for AI Coding Agents

Version Downloads Patterns AI-specific Runs locally

中文说明 ↓

When one of your AI agents does something you have to answer for, can you produce the record of what it saw, decided, and did? Your AI coding agent can already run shell commands, reach your database, write to your repo, and call tools over MCP. Right now, in this workspace. DeepSweep is the layer that governs those actions and turns them into a record you can stand behind.

DeepSweep is the Agent Evidence Layer, a flight recorder and circuit breaker for AI agents. The full layer sits in front of your MCP servers, enforces your allow / deny / require-human rules on every tool call, and writes each decision to a signed, hash-chained log you can verify offline. Your data never leaves your machine, and when the regulator, insurer, or auditor asks, you have the tape.

This extension is the free, local first step. Run one command, DeepSweep: Review My Agent Environment, and in under a second you see every capability your agents have and every gap where they can act beyond what they should. No account, no cloud, nothing leaves your editor. It also flags what AI assistants get wrong as you type: prompt injection, hallucinated packages, leaked secrets, MCP misconfigs. It flags them the moment they land. Works with Antigravity, Trae, Devin Desktop, Cursor, GitHub Copilot, Claude Code, and any AI coding tool. 77 patterns. Sub-second. Zero configuration.

From review to record. The extension shows you what your agents can do, locally and free. The DeepSweep gateway records and enforces what they actually do. Signed, tamper-evident, offline-verifiable. Start here. Graduate to the record layer when an incident, an auditor, or the EU AI Act's reporting clock makes "we have the tape" the difference.

Start with one command, DeepSweep: Review My Agent Environment, and see the whole picture in under a second: every capability your agent has, and every gap where it can act beyond what it should. Free, local, no account, no cloud, nothing leaves your editor.

And because it all runs on your machine, DeepSweep catches what your AI agent got wrong first, privately, in your editor, before it ever reaches a pull request, a CI pipeline, or your security team's dashboard. Local-first means the review is your private safety net. Fix what you find quietly and ship clean. When you need the record instead of the fix, for an auditor, an insurer, or an incident report, the DeepSweep gateway is the tier that produces it.


See it in 20 seconds

Three surfaces, one record. Every line below is a real output from a governed run. Nothing staged.

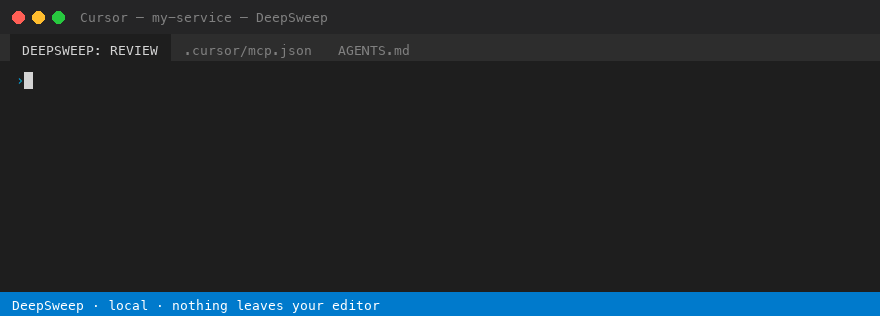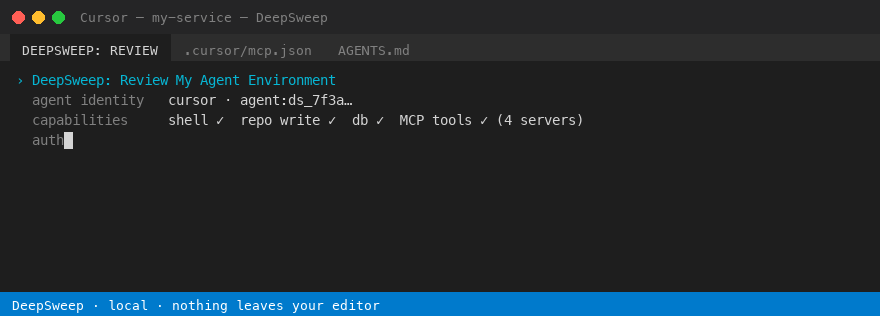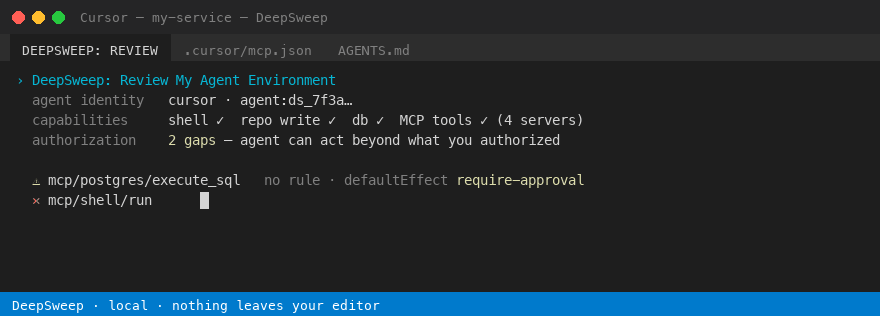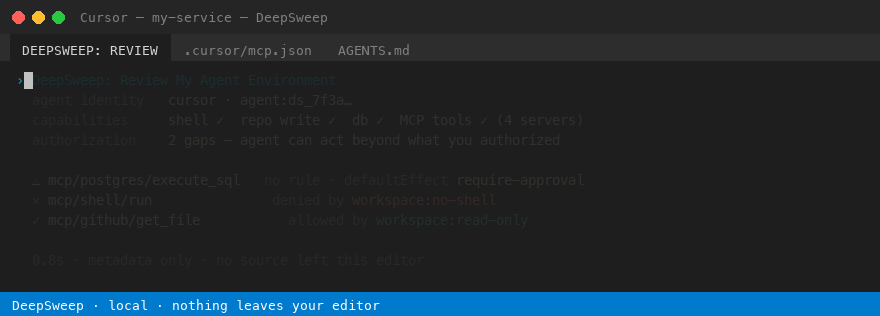
In your editor (Antigravity, Trae, Devin Desktop, Cursor, VS Code, Cline, Copilot): one command maps what each agent can do and where it acts beyond what you authorized.

DeepSweep: Review My Agent Environment inside a VS Code-family editor. Capabilities, authorization gaps, allowed/denied tool calls

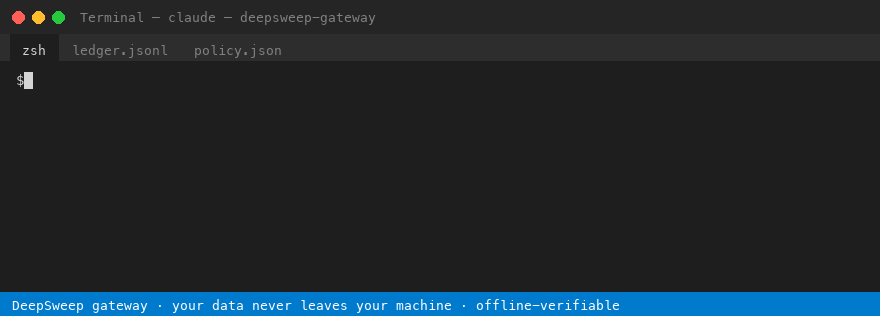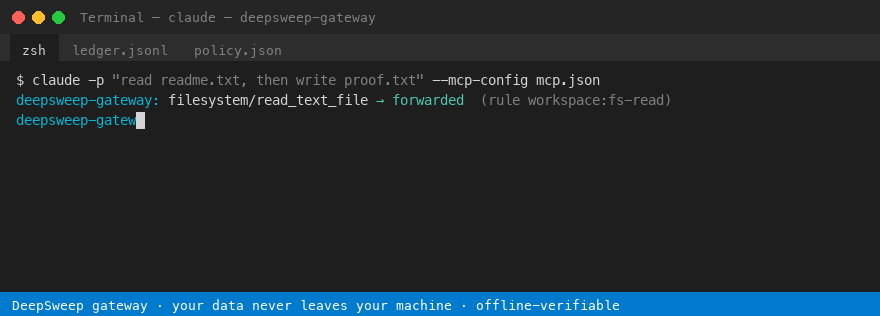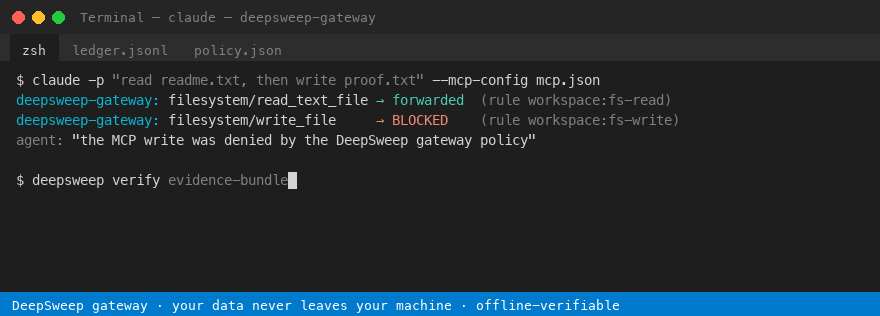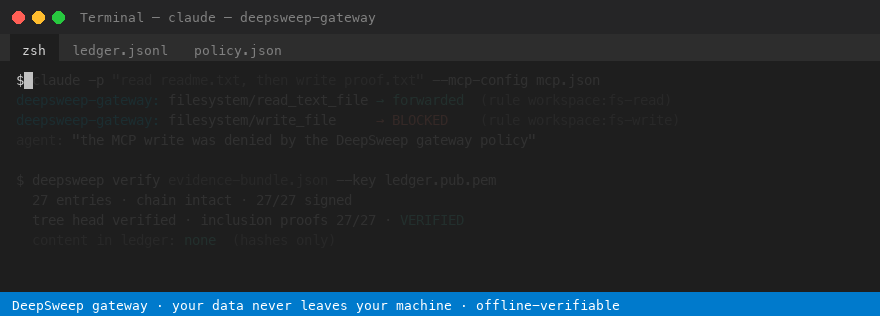
In the terminal (Claude Code, OpenAI Codex, Aider): the agent's MCP calls pass through the gateway. A write it isn't authorized to make is denied, and the whole session verifies offline.

A real Claude Code session through the DeepSweep gateway. Read forwarded, write BLOCKED, 27 signed ledger entries, VERIFIED offline

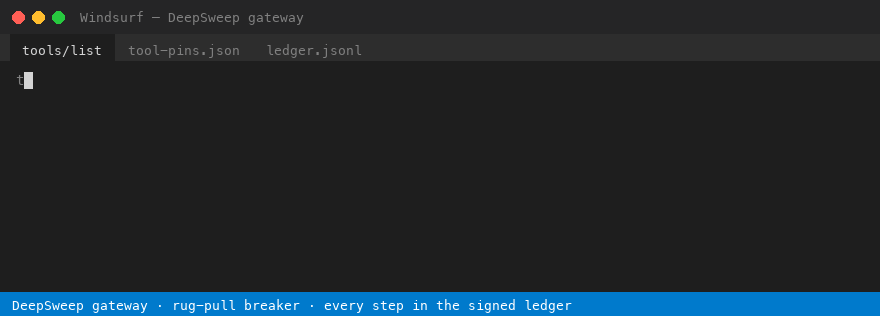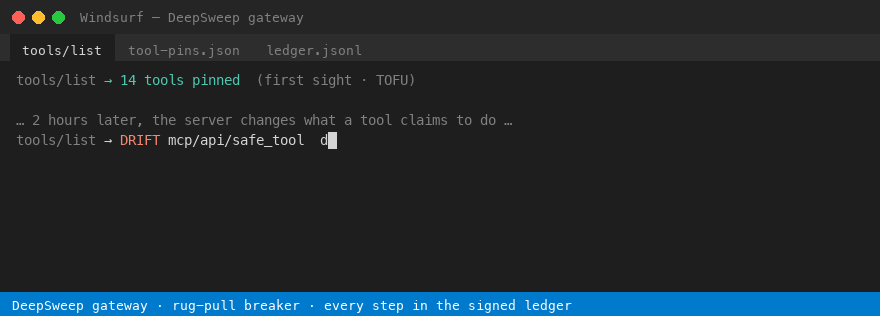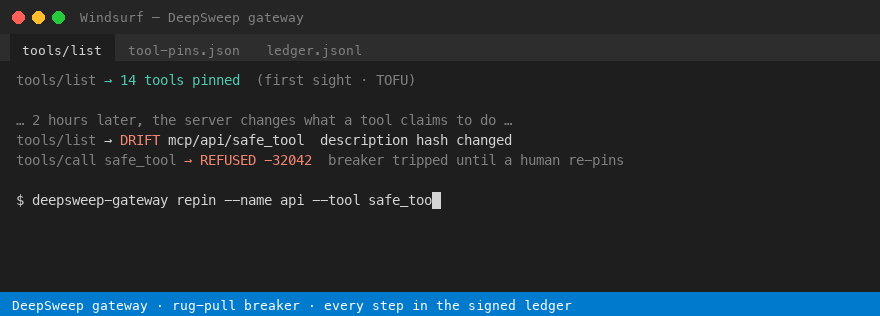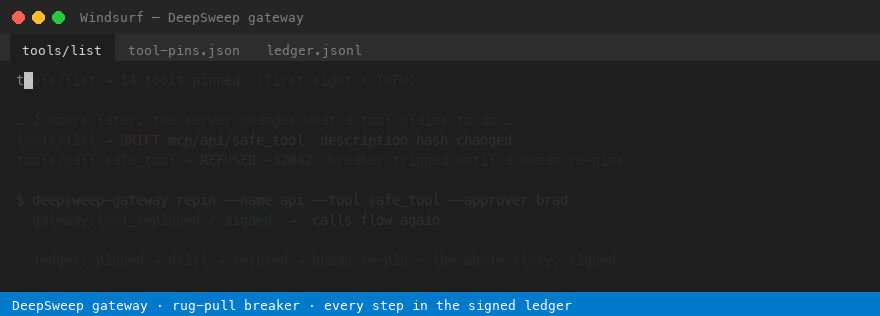
When a tool changes what it claims to do (any MCP client): the description drifts, the breaker trips, a human re-pins. Every step is in the signed ledger.

Rug-pull breaker: tools pinned on first sight, drift detected, calls refused until a human re-pins, all signed


Review My Agent Environment

AI coding agents quietly accumulate capabilities you never explicitly granted. MCP servers with broad tool access, shell execution, database reach, repository write, deploy hooks. DeepSweep: Review My Agent Environment maps them in a single local pass:

  • [CAPABILITIES] Detects what the agent can actually do: MCP tool access, shell execution, database access, repository write, deploy. It reads your workspace config (.cursorrules, mcp.json, agent settings). Metadata only. No source ever leaves the editor.
  • [IDENTITY] Derives a deterministic local agent identity, so the review is stable and reproducible from one run to the next.
  • [GAPS] Evaluates an advisory authorization policy and surfaces every gap where the agent can act beyond what it should, as findings you can read and act on. It advises rather than blocks.

Runs fully on-device in under a second. No account, no cloud, no upload. Free.

The Review is the free on-ramp to agent authorization. That means knowing which agent is authorized to do what, and where it acts beyond that. Behavioral-Firewall enforcement is where authorization is carried through. The Review is how you start, local-first and at no cost.


Catch what AI assistants miss, as you type

Beyond the one-time environment review, DeepSweep watches every change your AI assistant makes and flags risk the moment it lands.

Traditional SAST tools (Snyk, SonarQube, Semgrep) check hand-written code against hand-written rules. They were not designed for what happens when an AI agent generates, pastes, or modifies code in your editor.

DeepSweep reads the agent's environment as well as the code it produced. It detects the things AI assistants consistently get wrong. Prompt injection in rules files, hallucinated dependencies, hardcoded secrets pasted from example code, MCP tool-access misconfigurations, and Unicode backdoors that look invisible to humans but execute faithfully at runtime.

  • [VERIFY] Checks every save and keystroke (800 ms debounce). No CI wait.
  • [LOCAL] Pattern matching runs entirely on your machine. Source never leaves the editor.
  • [AGENTIC] AI-specific patterns with CVE references. They cover the .cursorrules, mcp.json, and agent-config attack surface.

Quick Start

  1. Install. Search DeepSweep in the Extensions view and click Install. In Cursor, where the extension index does not list us, use the one-minute package steps at deepsweep.ai/install/cursor instead.
  2. Review your agent. Run DeepSweep: Review My Agent Environment from the Command Palette to see your agent's capabilities and authorization gaps.
  3. Open a project. DeepSweep then checks AI-generated code automatically on open and on save.
  4. Fix findings. Click any finding for a one-line fix hint, or copy a remediation prompt and paste it back to your AI assistant.

Keyboard: Cmd+Shift+S (macOS) / Ctrl+Shift+S (Windows/Linux) to check the current file.


What It Detects

Category Examples Severity
Agent Authorization Gaps Agent can reach MCP tools, shell, database, repo write, or deploy beyond its intended scope High
Rules File Backdoors Invisible Unicode, bidirectional text overrides, hidden instructions in .cursorrules Critical
Prompt Injection Instruction override, role reassignment in agent-config files Critical
Credential Exposure Hardcoded API keys, AWS secrets, Stripe keys, private keys Critical
Data Exfiltration Code or secrets routed to external URLs via rules files Critical
MCP Security Unrestricted tool access, remote server connections, missing sandboxing High
Supply Chain Hallucinated packages, typosquatted dependencies, slopsquatting High
Injection Flaws SQL injection, XSS, command injection, path traversal High
Misconfigurations Insecure crypto, disabled TLS verification, debug mode in production Medium

77 patterns total. 37 are AI-specific and agentic-code-aware (prompt injection, MCP, rules-file, exfiltration, config). The other 40 are traditional security patterns.


Features

  • Review My Agent Environment. One-command local review of your agent's capabilities, identity, and authorization gaps (no account, no cloud)
  • Live Checks. Analyzes AI-generated code as you type, with an 800 ms debounce
  • Certify-on-Write. Catches an AI agent the moment it writes a new critical/high finding, with one-click Revert / Auto-Fix
  • Verification Proof. See exactly what was checked: patterns, files, categories, duration
  • 9 UI Surfaces. Status bar, Problems panel, CodeLens, Quick Fix, tree view, webview, decorations, notifications, output channel
  • AI Assistant Detection. Identifies which tool generated the code (Cursor, Copilot, Claude, Devin Desktop)
  • Finding Suppression. Suppress with reason categories, expiration dates, and audit trails
  • Fix All Auto-Correct. One-click static fixes across your workspace
  • Security Badge. Copy a shields.io-style badge for your README
  • Config File Monitoring. Auto-rechecks when .cursorrules, .env, or mcp.json change

Pricing

Free Pro Team
Agent Environment Review Yes Yes Yes
Code checks Unlimited Unlimited Unlimited
Patterns 77 77 77
Fix hints Yes Yes Yes
Full fix prompts — Yes Yes
Finding suppression Session only Persistent Persistent + audit trail
Security badge Basic Yes Yes
Fix All auto-correct — Yes Yes
Price $0 $19/mo $99/mo

The Repo Grade, the AI Code Health Score, and the Agent Environment Review are free forever. Paid tiers gate the fixes, never the grade. All checks run locally. No code is sent to external servers for pattern matching.


About: Agent Authorization

Model alignment is a statistical promise. It is not a per-action proof. An aligned coding agent can still silently delete a permission check, paste a hardcoded credential, or write a .cursorrules file that hides instructions in invisible Unicode. It can also act on your shell, your database, and your repo while doing it.

DeepSweep answers the question alignment can't: which agent is authorized to do what, and where is it acting beyond that? It starts with a free, local review of your agent's capabilities and authorization gaps, and carries that authorization through to the point where actions actually land. That turns "we hope it behaves" into "we can see and prove what it did."

This extension is the reference implementation. The full argument lives in the book:

The Authorized Agent: Identity, Authorization, and Audit for AI Agents in Production Book One in the DeepSweep.ai Thesis series, by Brad McEvilly.


Coming Soon: Agent Interoperability Bridge

DeepSweep is building the security layer for the AI agent protocol stack.

  • A2A Agent Card Review: security patterns for the Agent2Agent (A2A) protocol
  • Cross-Protocol Risk: when an MCP server is flagged, see which A2A workflows are affected

In development. No pattern is announced here until it ships.


Requirements

  • Any VS Code-compatible editor on 1.74.0 or newer: VS Code, Antigravity, Trae, Devin Desktop (formerly Windsurf), Cursor, Kiro, VSCodium, code-server
  • Node.js runtime (included with your editor)

Getting it into Cursor takes one extra step. DeepSweep runs in Cursor exactly as it does anywhere else, but Cursor's extension index does not list it, so searching the Extensions panel there will not find it. Download the package and add it from the panel's ... menu instead. It takes about a minute, no terminal: deepsweep.ai/install/cursor.

Every editor's current install path is at deepsweep.ai/install.


Commands

Command Description
DeepSweep: Review My Agent Environment Review your AI agent's capabilities, identity, and authorization gaps
DeepSweep: Review Project Check the entire workspace
DeepSweep: Review Current File Check the active file
DeepSweep: Copy Fix Prompt Copy remediation prompt for your AI assistant
DeepSweep: Fix All (Auto-Correct) Apply all static fixes
DeepSweep: Copy Security Badge Copy badge markdown for your README
DeepSweep: Sign In with GitHub Enable fix hints and dependency checks

Privacy

DeepSweep runs pattern matching and the agent-environment review locally in your editor. No source code is sent to external servers for analysis. Anonymous usage telemetry helps improve detection accuracy and can be disabled in settings.

Air-gapped? Set DEEPSWEEP_OFFLINE=1. With it set, DeepSweep originates no network requests of any kind. No telemetry, no dependency check, no sign-in, nothing. The review itself is unaffected: patterns, findings, diagnostics, code lenses, the grade and the fixes all run on your machine and always did. Offline mode costs you exactly two things: the dependency check, which needs a package registry to answer, and signing in, which needs an account service.

Telemetry off-switch: set DEEPSWEEP_TELEMETRY=off before launching your editor and DeepSweep sends no telemetry at all. No analytics, no diagnostics, no telemetry network calls. For CI machines and corporate policy. Works in every supported editor.

Diagnostics never carry your file paths. When something goes wrong, DeepSweep records the kind of problem: a file it could not read, a request that timed out. It never records the message itself, so folder names, project names and your username stay on your machine.

Privacy Policy


Autonomous agent workspaces (Devin and similar)

DeepSweep also runs where no human is watching. In autonomous agent environments such as Devin, add DeepSweep to the machine snapshot the same way you'd install any editor extension. It activates with the workspace, reviews the agent environment on open, and re-checks files as the agent writes them, exactly as it does under a human's hands. The agent's workspace gets the same review a developer's would: prompt injection in rules files, hallucinated dependencies, leaked secrets, MCP misconfigurations, caught in the environment where the agent is actually working, before its output ships.

It runs inside a Devin session with no special configuration beyond installing the extension into the snapshot.


Human Security Audit

When a review surfaces something you want a second opinion on, or you want your agent setup checked before it ships, a DeepSweep human security audit goes deeper than any automated pass. A security engineer reviews your agent configuration, permissions, and toolchain against a fixed-scope checklist and delivers a written report with clear [PASS] / [WARN] / [FAIL] findings and the exact steps to fix each one.

Audits start at $99, and if we find no critical issues, it's free. Book directly from the review panel in your editor, or at deepsweep.ai/audit.


Links

  • Website
  • Install guide, per editor
  • Human Security Audit

This page is the body of two listings, so both are named here. One codebase, one release, two registries:

  • VS Code Marketplace serves VS Code and Trae (changelog)
  • Open VSX serves Antigravity, Trae, Kiro, VSCodium, code-server, and the package Cursor and Devin Desktop install from (changelog)

DeepSweep — AI 编码智能体的运行时治理

English ↑

DeepSweep 为 AI 编码智能体提供运行时治理:审查每个智能体能做什么,帮助你授权它应该做什么,并治理它实际做了什么——在 AI 助手出错的那一刻(提示注入、幻觉依赖包、泄露的密钥、MCP 配置错误)就当场捕获,赶在问题进入生产环境之前。支持 Antigravity、Trae、Devin Desktop、Cursor、GitHub Copilot、Claude Code 以及任何 AI 编码工具。77 条检测模式,亚秒级响应,零配置。

从一条命令开始——DeepSweep: Review My Agent Environment(审查我的智能体环境)——一秒内看清全局:你的智能体拥有的每一项能力,以及它可能越权行动的每一个缺口。免费、本地运行、无需账号、无需云端,任何内容都不会离开你的编辑器。

因为一切都在你的机器上运行,DeepSweep 会最先、私密地、在你的编辑器里发现 AI 智能体犯的错——早于 Pull Request、早于 CI 流水线、早于安全团队的仪表盘。本地优先意味着它是你的安全网,而不是你的"记录在案":安静地修好,第一次就干净地交付。


审查我的智能体环境(Review My Agent Environment)

AI 编码智能体会悄悄积累你从未明确授予的能力——拥有广泛工具访问权的 MCP 服务器、Shell 执行、数据库访问、仓库写入、部署钩子。DeepSweep: Review My Agent Environment 在一次本地遍历中把它们全部映射出来:

  • 【能力】 通过读取工作区配置(.cursorrules、mcp.json、智能体设置)检测智能体实际能做什么——MCP 工具访问、Shell 执行、数据库访问、仓库写入、部署。只读取元数据;源代码永远不会离开编辑器。
  • 【身份】 派生确定性的本地智能体身份,使每次审查结果稳定、可复现。
  • 【缺口】 评估一份建议性授权策略,标出智能体可能越权行动的每一个缺口——以可读、可处理的发现呈现,而不是阻断你工作的强制拦截。

完全在设备端运行,耗时不到一秒。无需账号、无需云端、无需上传。免费。

这份审查是通往智能体授权的免费入口——知道哪个智能体被授权做什么、它在哪里越了权。行为防火墙(Behavioral Firewall)负责把授权贯彻到底;而审查是你的起点,本地优先、零成本。


在你打字的同时,捕获 AI 助手漏掉的问题

除了一次性的环境审查,DeepSweep 还会关注 AI 助手做出的每一次改动,在风险落地的那一刻立即标记。

传统 SAST 工具(Snyk、SonarQube、Semgrep)用手写规则检查手写代码。它们并不是为"AI 智能体在编辑器里生成、粘贴、修改代码"这一新场景设计的。

DeepSweep 读取智能体的运行环境,而不仅仅是它生成的代码。它检测 AI 助手持续犯错的那些问题——规则文件中的提示注入、幻觉依赖、从示例代码粘贴进来的硬编码密钥、MCP 工具访问配置错误,以及人眼不可见、运行时却忠实执行的 Unicode 后门。

  • 【验证】 每次保存和输入都会检查(800 毫秒防抖)。无需等待 CI。
  • 【本地】 模式匹配完全在你的机器上运行。源代码永远不会离开编辑器。
  • 【智能体感知】 附带 CVE 参考的 AI 专属模式,专为 .cursorrules、mcp.json 和智能体配置这一攻击面而构建。

快速开始

  1. 安装 —— 在扩展视图中搜索 DeepSweep,点击 Install。在 Cursor 中,扩展索引尚未收录 DeepSweep,请改用 deepsweep.ai/install/cursor 上约一分钟的安装包步骤。
  2. 审查你的智能体 —— 在命令面板运行 DeepSweep: Review My Agent Environment,查看智能体的能力与授权缺口。
  3. 打开一个项目 —— DeepSweep 会在打开与保存时自动检查 AI 生成的代码。
  4. 修复发现 —— 点击任一发现即可获得一行修复提示,或复制修复提示词,粘贴回你的 AI 助手。

快捷键:Cmd+Shift+S(macOS)/ Ctrl+Shift+S(Windows/Linux)检查当前文件。


检测范围

类别 示例 严重度
智能体授权缺口 智能体可访问超出预期范围的 MCP 工具、Shell、数据库、仓库写入或部署 高
规则文件后门 不可见 Unicode、双向文本覆盖、.cursorrules 中的隐藏指令 严重
提示注入 智能体配置文件中的指令覆盖、角色重新分配 严重
凭据暴露 硬编码的 API 密钥、AWS 密钥、Stripe 密钥、私钥 严重
数据外泄 通过规则文件把代码或密钥发送到外部 URL 严重
MCP 安全 不受限的工具访问、远程服务器连接、缺失沙箱 高
供应链 幻觉依赖包、拼写抢注依赖(typosquatting / slopsquatting) 高
注入缺陷 SQL 注入、XSS、命令注入、路径穿越 高
错误配置 不安全加密、关闭 TLS 校验、生产环境开启调试模式 中

共 77 条模式 —— 37 条面向 AI 与智能体代码(提示注入、MCP、规则文件、外泄、配置),另有 40 条传统安全模式。


定价

Free Pro Team
智能体环境审查 有 有 有
代码检查 无限 无限 无限
检测模式 77 77 77
修复提示 有 有 有
完整修复提示词 — 有 有
发现抑制 仅当前会话 持久化 持久化 + 审计记录
安全徽章 基础 有 有
一键全部修复 — 有 有
价格 $0 $19/月 $99/月

仓库评级(Repo Grade)、AI 代码健康分和智能体环境审查永久免费。付费层级限制的是修复能力,永远不是评级本身。所有检查都在本地运行——不会把代码发送到外部服务器做模式匹配。


隐私

DeepSweep 的模式匹配与智能体环境审查在你的编辑器内本地运行。不会把源代码发送到外部服务器进行分析。匿名使用遥测用于改进检测准确率,可在设置中关闭。

隔离网络环境请设置 DEEPSWEEP_OFFLINE=1。 设置后,DeepSweep 不会发起任何网络请求——没有遥测、没有依赖检查、没有登录,什么都没有。审查本身不受影响:模式匹配、发现项、诊断、代码镜头、评级与修复建议全部在你的机器上运行,一向如此。离线模式只会失去两项功能:需要访问软件包注册表的依赖检查,以及需要账户服务的登录。

遥测开关: 在启动编辑器前设置环境变量 DEEPSWEEP_TELEMETRY=off,DeepSweep 将不发送任何遥测——没有分析、没有诊断、没有任何遥测网络请求。适用于 CI 机器与企业合规策略;在所有受支持的编辑器中均生效。

诊断信息永远不携带你的文件路径。 出现问题时,DeepSweep 只记录问题的类型——某个文件无法读取、某个请求超时——绝不记录消息内容本身,因此目录名、项目名和用户名都留在你的机器上。

隐私政策


自主智能体工作区(Devin 等)

DeepSweep 也能在无人值守的环境中运行。在 Devin 这类自主智能体环境中, 只需像安装任何编辑器扩展一样,把 DeepSweep 加入机器快照(machine snapshot)—— 它会随工作区启动,在打开时审查智能体环境,并在智能体写入文件时持续复查, 与在开发者手中的表现完全一致。它可在 Devin 会话中运行; 除了将扩展装入快照外,无需任何额外配置。


人工安全审计

当一次审查发现了你想要第二意见的问题,或者你希望在上线前对智能体配置做一次全面检查时,DeepSweep 人工安全审计 比任何自动化检查都更深入。安全工程师会依照固定范围的清单审查你的智能体配置、权限与工具链,并交付一份书面报告,用清晰的 [PASS] / [WARN] / [FAIL] 结论标注每项发现及对应的修复步骤。

审计 $99 起;如未发现严重问题,则完全免费。可直接在编辑器的审查面板中预约,或访问 deepsweep.ai/audit。


链接

  • 官网
  • 各编辑器安装指南
  • 人工安全审计

本页面同时作为两个市场列表的正文,因此两者都列在这里——同一套代码、同一个版本、两个注册表:

  • VS Code Marketplace —— 服务 VS Code 与 Trae(更新日志)
  • Open VSX —— 服务 Antigravity、Trae、Kiro、VSCodium、code-server,Cursor 与 Devin Desktop 也从这里获取安装包(更新日志)
  • Contact us
  • Jobs
  • Privacy
  • Manage cookies
  • Terms of use
  • Trademarks
  • Your Privacy Choices
  • Consumer Health Privacy
© 2026 Microsoft