
Auric Code Health — Secrets, TODOs & RiskLanguage-agnostic code-health scanning: hardcoded secrets and credential URLs, TODO/FIXME markers, debug leftovers, merge conflict markers, risky APIs, injection and TLS-bypass patterns, and oversized files with 60+ stable fine-grained signatures and redacted evidence. Searchable rulebooks plus heal Installation Launch VS Code Quick Open ( Ctrl+P), paste the following command, and press enter.Copied to clipboard |

Auric Code Health — Secrets, TODOs & Risk
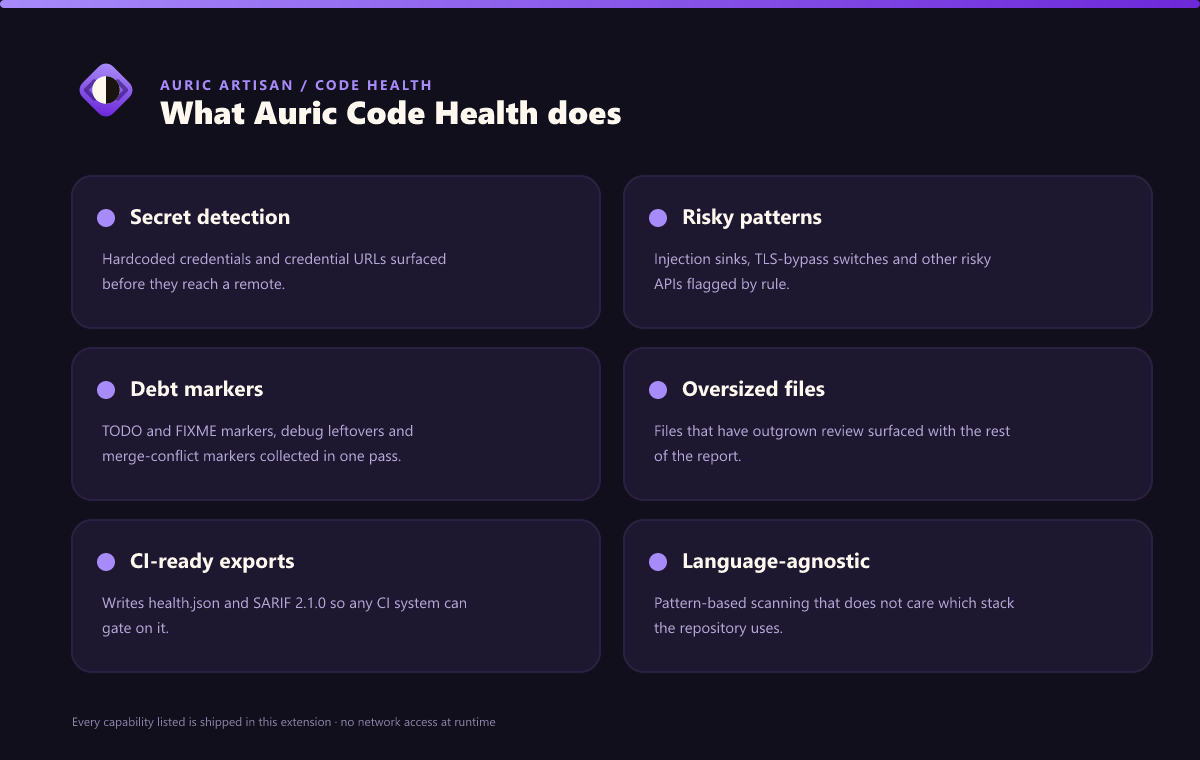
A language-agnostic hygiene scanner for every file in your repo — hardcoded
secrets, injection and TLS-bypass patterns, debug leftovers, merge markers, TODOs,
and oversized files. Exports Auric Code Health reads source text with argument-aware structured analysis (no
AST, no git-history scan, no dependency), so it favours precision — it catches the
common, high-confidence cases and tells a constant from a dynamic value. It runs on
every language, and the exact same engine powers the Every detector now has a stable fine-grained rule identity, detector version, confidence, automation method, remediation, and requirement/source links. Possible secret evidence is redacted before it reaches reports, SARIF, Studio, or history. Features
Seven hygiene categories
Because it's argument-aware, Code Health StudioOpen Code Health Studio for the dedicated health score and grade, all seven
category counts, confidence-aware findings, category/confidence/text filters, and
direct actions for re-scanning, the project report, Searchable Code Health rulebookThe local Knowledge Base maps the fine-grained signatures into a searchable
Code Health rulebook with evidence/confidence policy, suppression governance,
secret-response guidance, glossary terms, and official OWASP/CWE/NIST provenance.
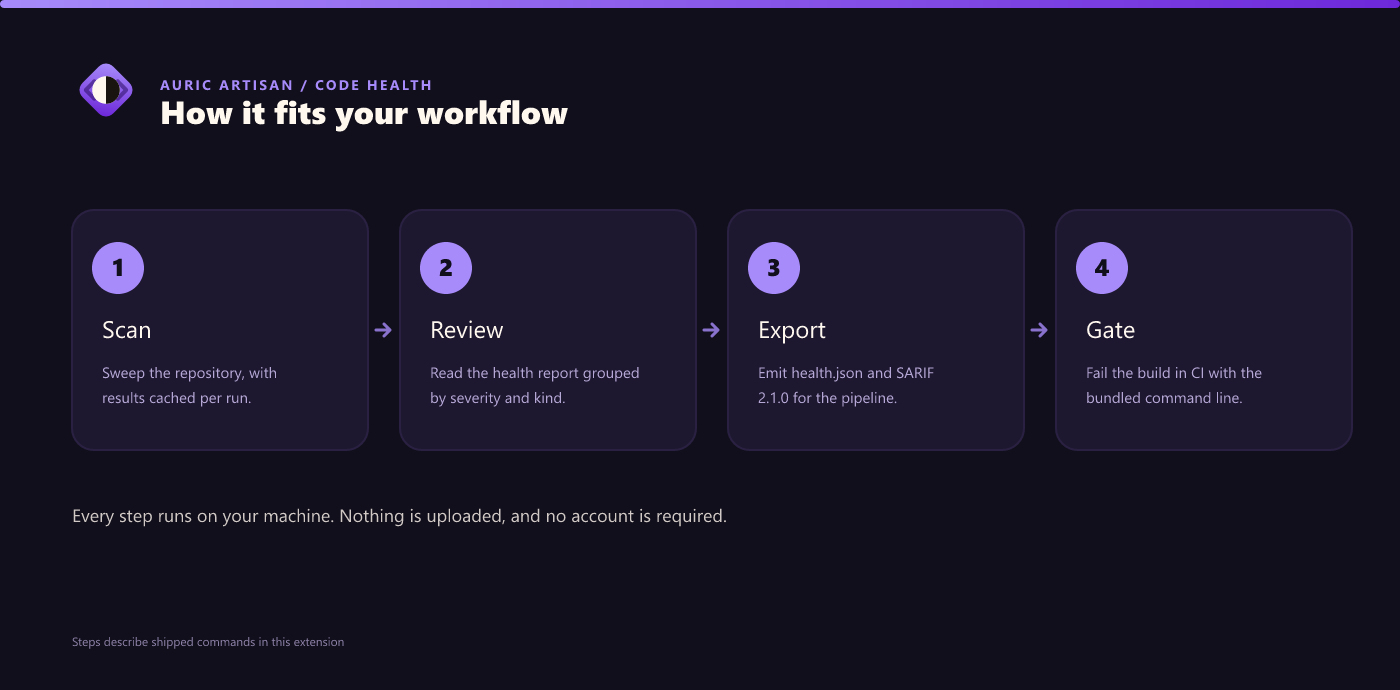
Generate Health records for CI —
|
| Title | Command id | Keybinding |
|---|---|---|
| Workstation: Command Center | auricCodeHealth.commandCenter |
Ctrl+Alt+. (Cmd+Alt+.) |
| Open Code Health Studio | auricCodeHealth.openStudio |
|
| Open Rulebook & Knowledge Database | auricCodeHealth.openKnowledgeBase |
|
| Build Workspace Knowledge Database (JSON + Markdown) | auricCodeHealth.writeKnowledgeDatabase |
|
| Open Unified Icon Studio | auricCodeHealth.openIconStudio |
|
| Generate Project Health Report (Color, A11y & Code Health) | auricCodeHealth.projectHealthReport |
|
| Write Health Record (health.json + SARIF) | auricCodeHealth.writeHealthReport |
|
| Generate Agent-Ready Remediation Plan | auricCodeHealth.generateAiPlan |
|
| Clear Workspace Scan Cache | auricCodeHealth.clearScanCache |
|
| Open Workspace Data Folder | auricCodeHealth.openDataFolder |
All commands are listed in the palette under the Auric Artisan category.
Keybindings
| Keybinding | Command |
|---|---|
Ctrl+Alt+. / Cmd+Alt+. |
Workstation: Command Center — a native QuickPick with Suggested actions, top findings, and workspace artifacts (health.json, plan, project report). |
Settings
A representative subset — there are 28 settings under the auricCodeHealth.
namespace (open Settings and search auricCodeHealth).
| Setting | Default | Description |
|---|---|---|
auricCodeHealth.codeHealth.enabled |
true |
Master switch for the code-health scan. |
auricCodeHealth.codeHealth.secret |
true |
Detect possible hardcoded secrets. |
auricCodeHealth.codeHealth.security |
true |
Detect injection, TLS-bypass, and other security footguns. |
auricCodeHealth.codeHealth.customSecretPatterns |
[] |
Extra org-specific secret regexes. |
auricCodeHealth.health.formats |
["json","sarif","history"] |
Which health records to write. |
auricCodeHealth.health.writeOnScan |
true |
Write the health record automatically after a scan. |
auricCodeHealth.data.folderName |
.auric-artisan |
Workspace data folder name. |
auricCodeHealth.scan.maxFiles |
4000 |
Cap on files read per scan (truncation is reported). |
Part of the Auric Artisan Workstation
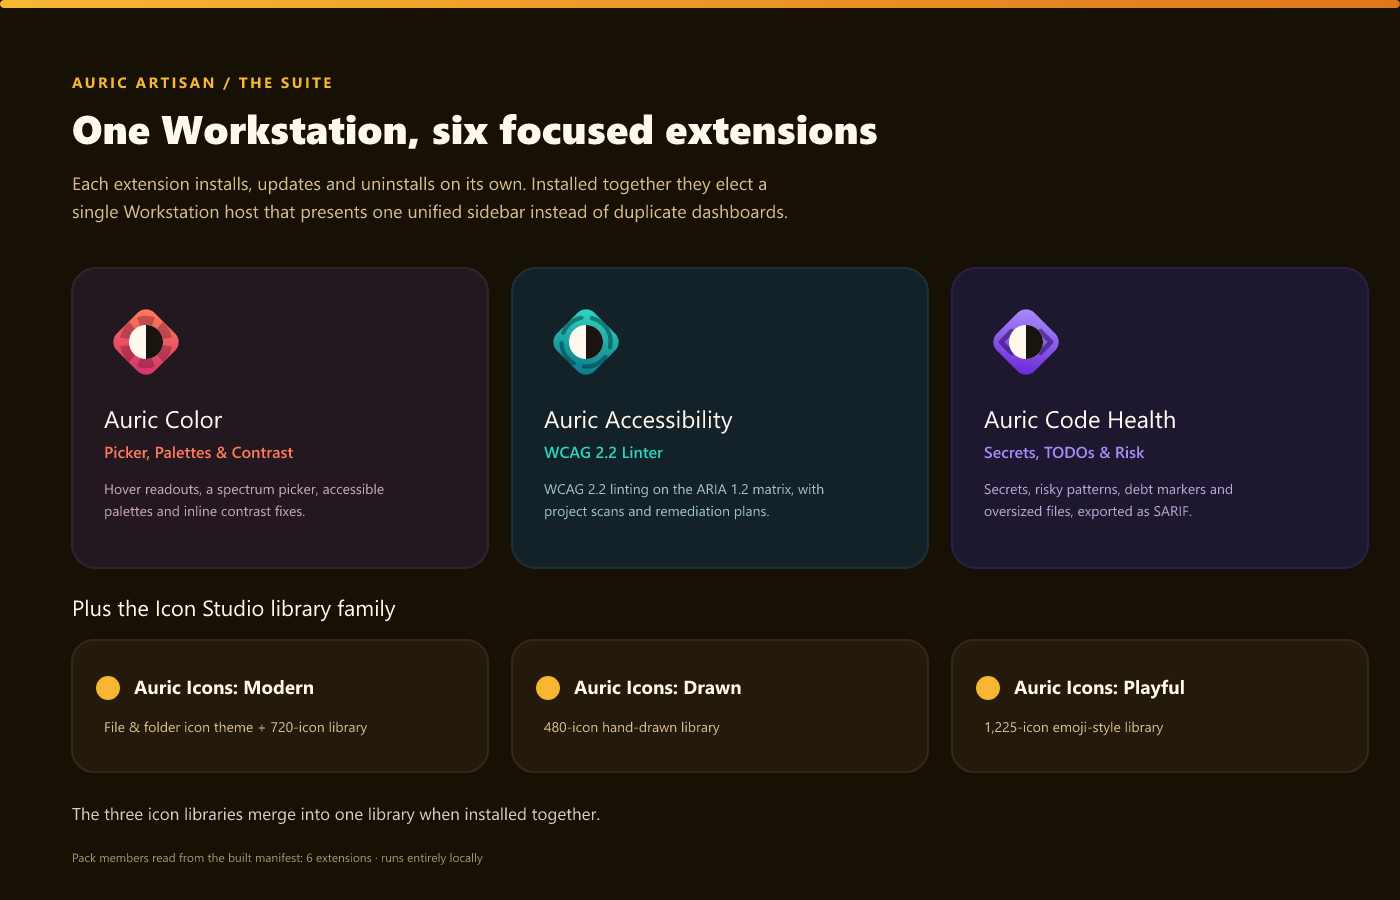
Installed on its own, Auric Code Health is a complete product with an Overview home and a dedicated Code Health Studio for filtering and acting on the full report.
Install it alongside Auric Accessibility and/or Auric Color and the three cooperate automatically. The suite elects a single Workstation host (priority Accessibility → Color → Code Health); with a sibling present, Code Health contributes its Code Health tab, hygiene score, findings, and actions into that host's capability-aware Studio and Command Center instead of showing a second dashboard, and its diagnostics keep running as the single owner of code-health analysis. The election updates live on install/uninstall, no reload.
Privacy
Everything runs locally. Auric Code Health sends no source code, scan results, or
telemetry to any server — the no-network guarantee is mechanically enforced against
the shipped build, and the CLI runs the same way. Health records and the remediation
plan are written only to the workspace .auric-artisan/ folder. No account, no API
key, no paid tier.
Requirements
- VS Code 1.74 or newer. Works in single-folder and multi-root workspaces.
By Auric Artisan · auricartisan.com