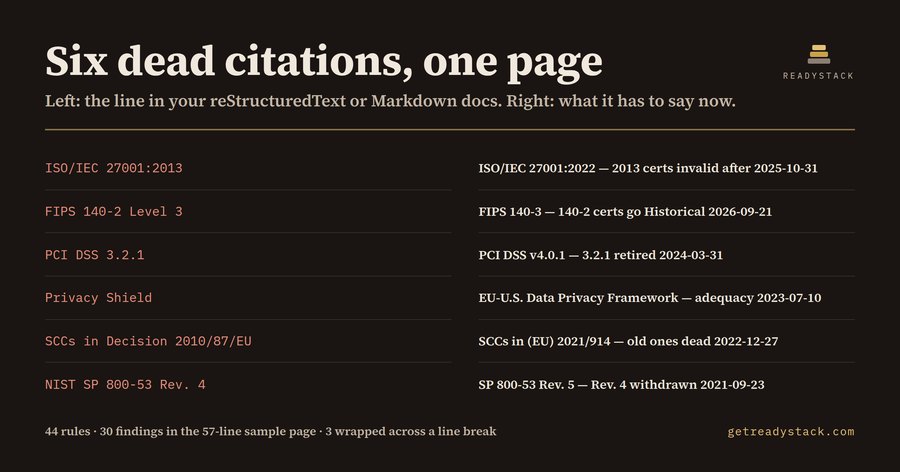
Stale Standard Citation LintFinds superseded standard editions and repealed laws cited in your .rst/.md docs — ISO 27001:2013, PCI DSS 3.2.1, FIPS 140-2, Privacy Shield, the old SCCs — with the date each one died. Installation Launch VS Code Quick Open ( Ctrl+P), paste the following command, and press enter.Copied to clipboard |

Stale Standard Citation Lint
Your security page still says ISO/IEC 27001:2013. That edition stopped being certifiable on 2025-10-31, and the person reading the page is a procurement reviewer, not a friend. This extension reads a reStructuredText, Markdown or plain text document and reports every standard edition, framework version and legal instrument in it that has been superseded, withdrawn or repealed. Each finding carries three things: what you wrote, what replaces it, and the date the old one stopped being true — counted against the day you run the check, not against the day the rule was written. What it finds44 rules, grouped:
Why not grepreStructuredText is hard-wrapped. In the sample page shipped with this extension, 3 of the 30 findings are citations that the wrapper split across a line break — The other half is that grep does not know dates. Free and paidChecking the document open in your editor is free and complete. All 44 rules, every finding, every replacement date, no licence key, no cap on runs. A file you check is a file you are done with. The licence covers a different job, not a bigger helping of the same one: sweeping every For comparison: GRC consultants bill $150-$300 an hour for documentation review, and one dense compliance page rarely takes under an hour. Commands
Run it without installing anythingThe same engine, the same 44 rules, in a browser: https://getreadystack.com/tools/stale-standard-citation-lint Limits worth knowingIt matches citations as they are written. A standard referred to only by nickname ("the old ISO standard") is invisible to it. It does not read your certificate, so it cannot tell you whether your ISO/IEC 27001:2022 audit actually happened — only that the sentence in your docs describes an edition that still exists. |