PII-in-Logs Lint (console.log(req.body))Names every line where your Node/TypeScript service writes personal data into logs, crash reports and analytics: console.log(req.body), pino without redact, sendDefaultPii: true. 22 rules. Installation Launch VS Code Quick Open ( Ctrl+P), paste the following command, and press enter.Copied to clipboard |

PII-in-Logs Lint
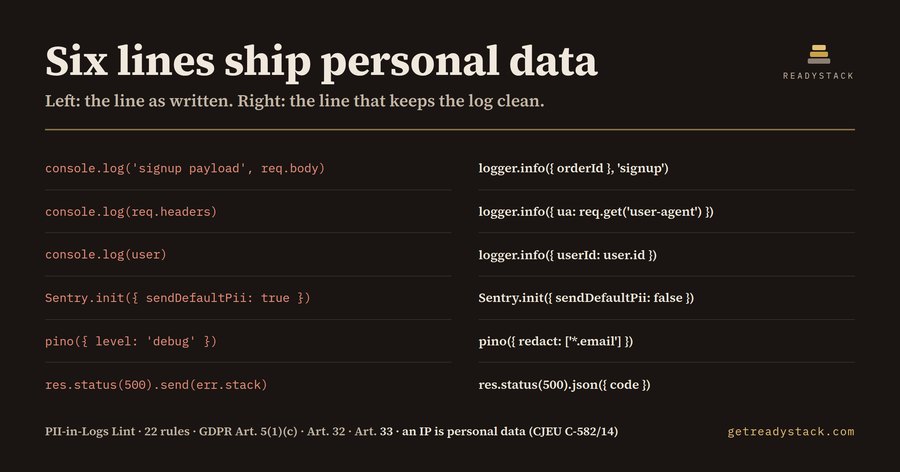
Finds the lines in a Node or TypeScript service that put personal data into a log, a crash report or an analytics call — and names the line, the rule and the one-line fix. The line it is built around is this one: Nothing is wrong with it at compile time, nothing is wrong with it in review, and it runs for years. What it does is copy every signup body — name, email, date of birth, sometimes a card — into stdout, from stdout into the log shipper, from the shipper into the vendor's index, and from the index into the backups. GDPR Art. 5(1)(c) says you collect the minimum; Art. 32 says you secure it; Art. 33 gives you 72 hours to notify a supervisory authority once you become aware that it leaked. The 72 hours start when someone notices the log, not when the line was written. A coding assistant writes that line by default. Asked to "add logging", it logs the object it has, because the object it has is the request. That is the gap this extension covers: the code compiles, the tests pass, and the personal data ships. What the 22 rules look for
An IP address is personal data in the EU — Breyer, CJEU C-582/14 — which is why Measured on the shipped fixturesTwo files ship with the source, one route each, same routes, different habits:
Run the check on both and compare the output; that is the whole behaviour of the tool. Free and paidFree, no key, no limit: the file you have open. Every offending line is marked in the editor with the rule, the article it touches and the fix. That answer is complete on its own — you can clean a file with it and never open the rest. Paid ($29 once): the same 22 rules across every The split is scope and ownership. Nothing is watermarked, nothing expires, no rule is withheld from the free file check. Using itTwo commands in the Command Palette: one checks the file in front of you, one sweeps the workspace. Findings appear as editor diagnostics and as a written report in the output channel. The rules live in YardstickGitHub Advanced Security lists at $49 per active committer per month ($30 Code Security + $19 Secret Protection) and looks for secrets — keys and tokens — not for the customer's name travelling in a log line. The same 22 rules run free, in the browser, on one file: https://getreadystack.com/tools/log-pii-telemetry-lint |