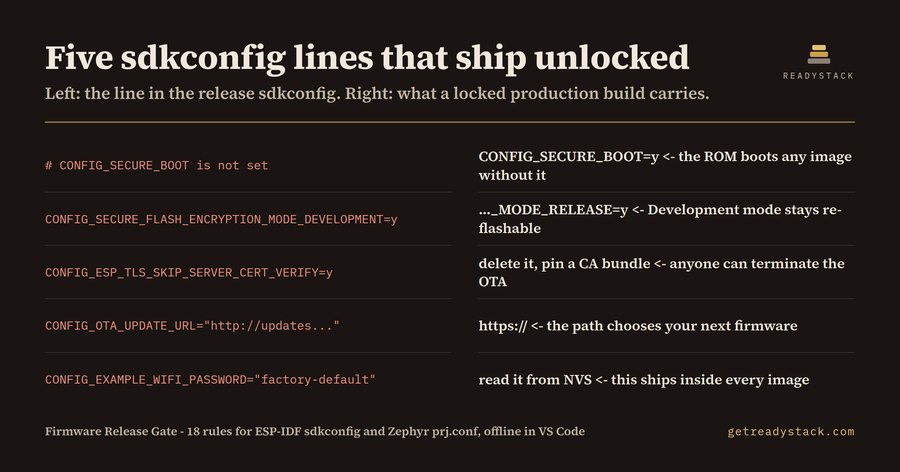
Firmware Release Gate for sdkconfig and prj.confFinds the build-config lines that ship an ESP-IDF or Zephyr device with secure boot off, a debug port open, unsigned images or plaintext OTA. Installation Launch VS Code Quick Open ( Ctrl+P), paste the following command, and press enter.Copied to clipboard |

Firmware Release Gate
Finds the build-config lines that ship an ESP-IDF or Zephyr device with secure boot off, a debug port open, unsigned images or plaintext OTA. What it findsWhat it does for free
With a licence
An outside firmware-only security review starts around $6,000 and a full IoT device assessment runs $10,000 to $50,000; this is the config pass you run before you pay for one. Get the full version - $29 - $29 once, one licence key per person or team seat, 7-day full refund. Full workspace sweep and report: free for 7 days from your first sweep, then a licence key. Install |