Consent Gate HTML Lint (EU/UK ePrivacy)Finds third-party script and iframe tags in your HTML that load trackers before the visitor consents — the prior-consent rule of EU/UK ePrivacy. Installation Launch VS Code Quick Open ( Ctrl+P), paste the following command, and press enter.Copied to clipboard |

Consent Gate HTML Lint (EU/UK ePrivacy)
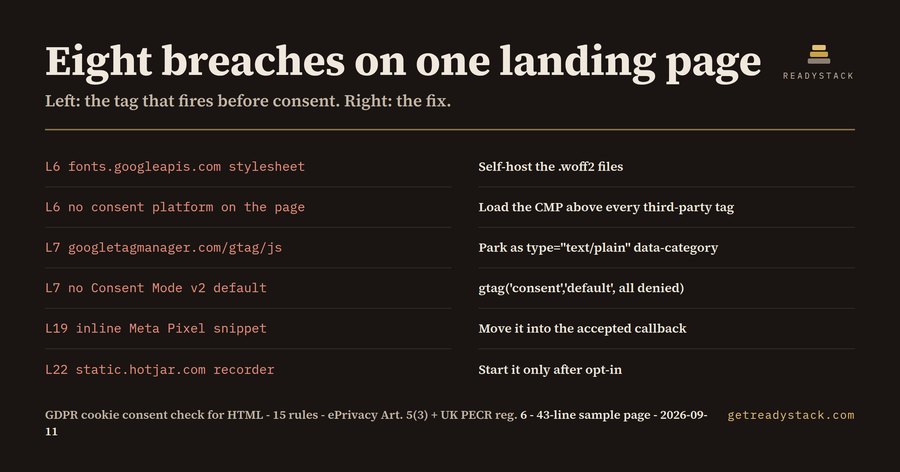
This extension reads an HTML file and reports every It exists because the prior-consent rule is a source-code rule. Article 5(3) of the ePrivacy Directive (2002/58/EC), as implemented by each member state, and regulation 6 of the UK PECR both say that storing or reading information on a visitor's device requires consent before it happens. A tag sitting in What it checks15 rules, all of them written in
A tag is treated as correctly gated when it carries Commands
Free and licensedChecking the file in front of you is free, with all 15 rules, no account and no usage limit. The workspace sweep and the dated report are the licensed part, because that is the artefact you hand to a client rather than the answer you need while typing. Licence: $29 once - one licence key per person or team seat. The yardstick below is what a single missed line has already cost an operator in court. The same 15 rules run, unchanged, in a single web page: https://getreadystack.com/tools/consent-gate-html-lint — paste markup, read findings, nothing is uploaded. What the mistake costsLandgericht München I, case 3 O 17493/20 of 20 January 2022, ordered a website operator to pay EUR 100 in damages to one visitor over a single hotlinked Google Fonts request. Under GDPR Article 83(5) the ceiling for the same class of breach is EUR 20 million or 4% of worldwide annual turnover. LimitsIt reads markup, not a running page. A tracker injected at runtime by a bundler, a tag manager container or a WordPress plugin is invisible to a source-level check; verify those in the browser. The rules describe EU/EEA and UK law only, and this is engineering tooling, not legal advice. |