Biometric Consent Audit (BIPA / CUBI / CO)Audits code that captures faces, fingerprints or voiceprints: missing written consent, missing destruction schedule, retention past the Illinois BIPA three-year cap, third-party disclosure. Installation Launch VS Code Quick Open ( Ctrl+P), paste the following command, and press enter.Copied to clipboard |

Biometric Consent Audit
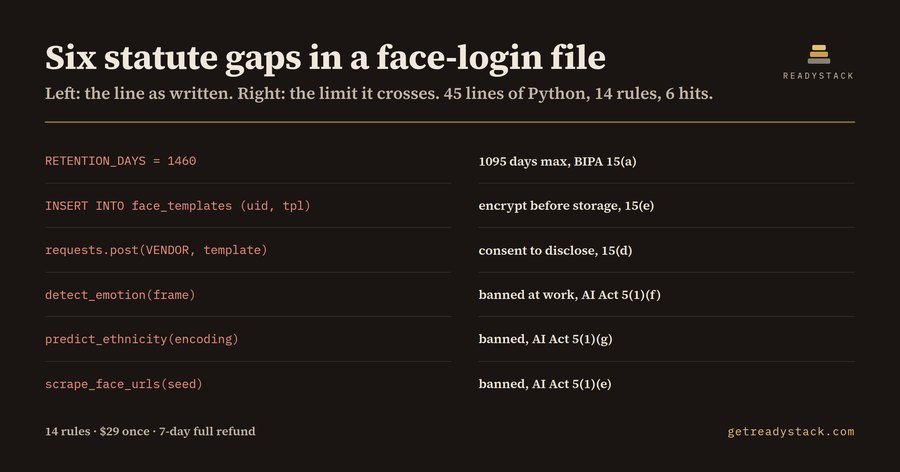
Static audit for code that captures a face, a fingerprint, an iris or a voiceprint. It reads one file at a time and reports the lines that a biometric-privacy statute reaches: the missing written release, the missing destruction schedule, retention past the three-year cap, the template that leaves the process, and the three biometric uses the EU AI Act prohibits outright. The 2026 question a reviewer actually asks about generated code is "does this obey the statute", not "does this lint". A formatter cannot answer it, because none of this is a style question. What it checks (14 rules)
Each finding prints the line number, the rule name and the subsection, so the output can be pasted straight into a review thread. Measured on the shipped fixtures
The retention rules are arithmetic, not pattern matching: ScaleThe audit date is a setting, so a file can be re-audited as of any date. A commercial audit that reaches the same subsections is billed by the hour: US privacy counsel charges roughly $400-$600 an hour for a pre-launch review of biometric code. Free and fullFree, no key: audit the file you have open, with every finding and subsection. Full version: scan the whole workspace and export a dated evidence report (Markdown + CSV) per file and per statute subsection - https://buy.polar.sh/polar_cl_ymzWuO9GRzRMb8YULAoIhzs4TnxmfVlQxtxEI0ax9oq Hub page: https://getreadystack.com/tools/biometric-consent-audit Not legal adviceThe rules cite the statutory text they implement. Whether a given system is in scope, and what a given deployment owes, is a question for counsel. |