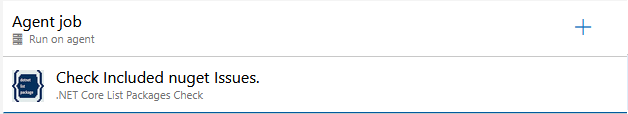
OverviewThe .NET Core List Packages Check task validates NuGet packages in your .NET projects by running dotnet list package commands during your build pipeline. It helps identify security vulnerabilities, deprecated packages, and outdated dependencies before they reach production. In a CI environment this task can be helpful to detect included NuGet packages that might pose an issue. Depending on configuration this can block the build pipeline whether you choose it or not. PrerequisitesThis extension supports Azure DevOps Server 2019 and Azure DevOps Online. VideoA comprehensive video demonstration of this extension is available at https://l.samayas.eu/g9r8vJrrxp How to useAfter installing the extension, add the .NET Core List Packages Check task to a new or existing build definition. Once you've added the .NET Core List Packages Check you should have the following:
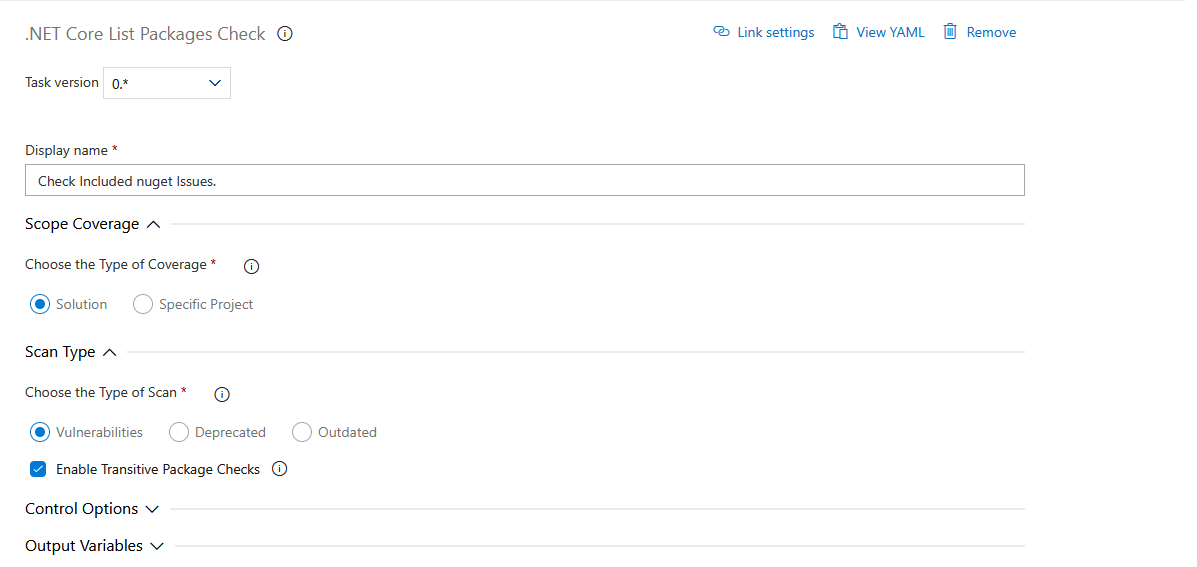
Once you've added the task to your Build pipeline you need to configure your individual task.
Inside your task configuration you have 2 distinct blocks that are important:
Scope CoverageUnder the Scope Coverage in essence you define on what the task is executed.
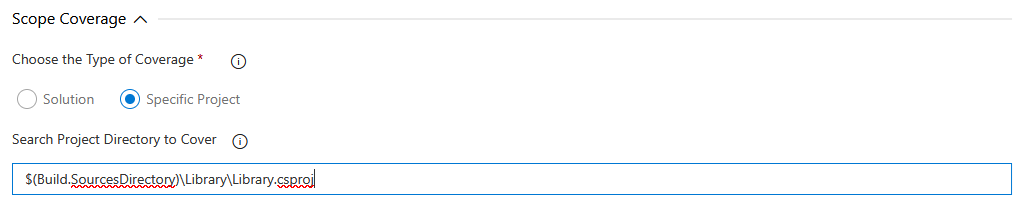
When having selected the Project scope an extra field will be available to enter the specified project.
The underlying command only supports solution or project and you can't have multiple projects scanned. Scan TypeIn the Scan Type you determine what type of scan is executed.
Each of these scan types are distinct and if you need a multitude you need to add this task multiple times. Enable Transitive Package Checks
Scan Type OutdatedWhen the scan Type is outdated there are 3 new options.
When Highest Minor or Highest patch is selected then Transitive scans wont be executed.
Build BehaviorThe task affects your pipeline outcome based on what it finds:
AdvancedThe Advanced section contains configuration options for customizing the task's working directory behavior. Solution Directory LocationThis parameter allows customization of the working directory where the task searches for the solution or project files. By default, the task uses $(Build.SourcesDirectory), which points to the root of the repository. This setting is useful when the solution file is not located in the root of the repository but instead resides in a subfolder. For example, if the solution is located in a src folder or a nested directory structure, this parameter can be adjusted to point to that specific location. Default Value: $(Build.SourcesDirectory) Usage Example: If the solution is located in a subfolder called /MyApplication, set this value to $(Build.SourcesDirectory)/MyApplication. Output ArtifactsAll scan results are saved to the pipeline workspace under nuget-audit: Depending on whether the Transitive scan is enabled or not this task will generate 2 or 4 files as output
If you choose to afterwards this can be added as an artifact on the build. TargetThe goal of this add-in is to detect potential issues with included Nuget packages. Version HistoryVersion 1.1 Solutions containing projects that dotnet restore cannot restore (no NuGet assets file afterwards, e.g. WiX setup projects mapped only to custom solution build types, or old-style project formats) no longer fail the scan. These projects are detected up front, reported as warnings, and the remaining projects are scanned individually. Version 1.0 Initial Version |